Nginx

Practical notes on using Nginx in real projects: web server and reverse proxy configuration, HTTPS and SSL/TLS certificates, redirects, routing, headers and production setups. I collect the problems I encounter in practice, how I diagnose them and the solutions that work.

740-requests-in-three-minutes-hardening-nginx-without-blocking-real-readers.png
Nginx

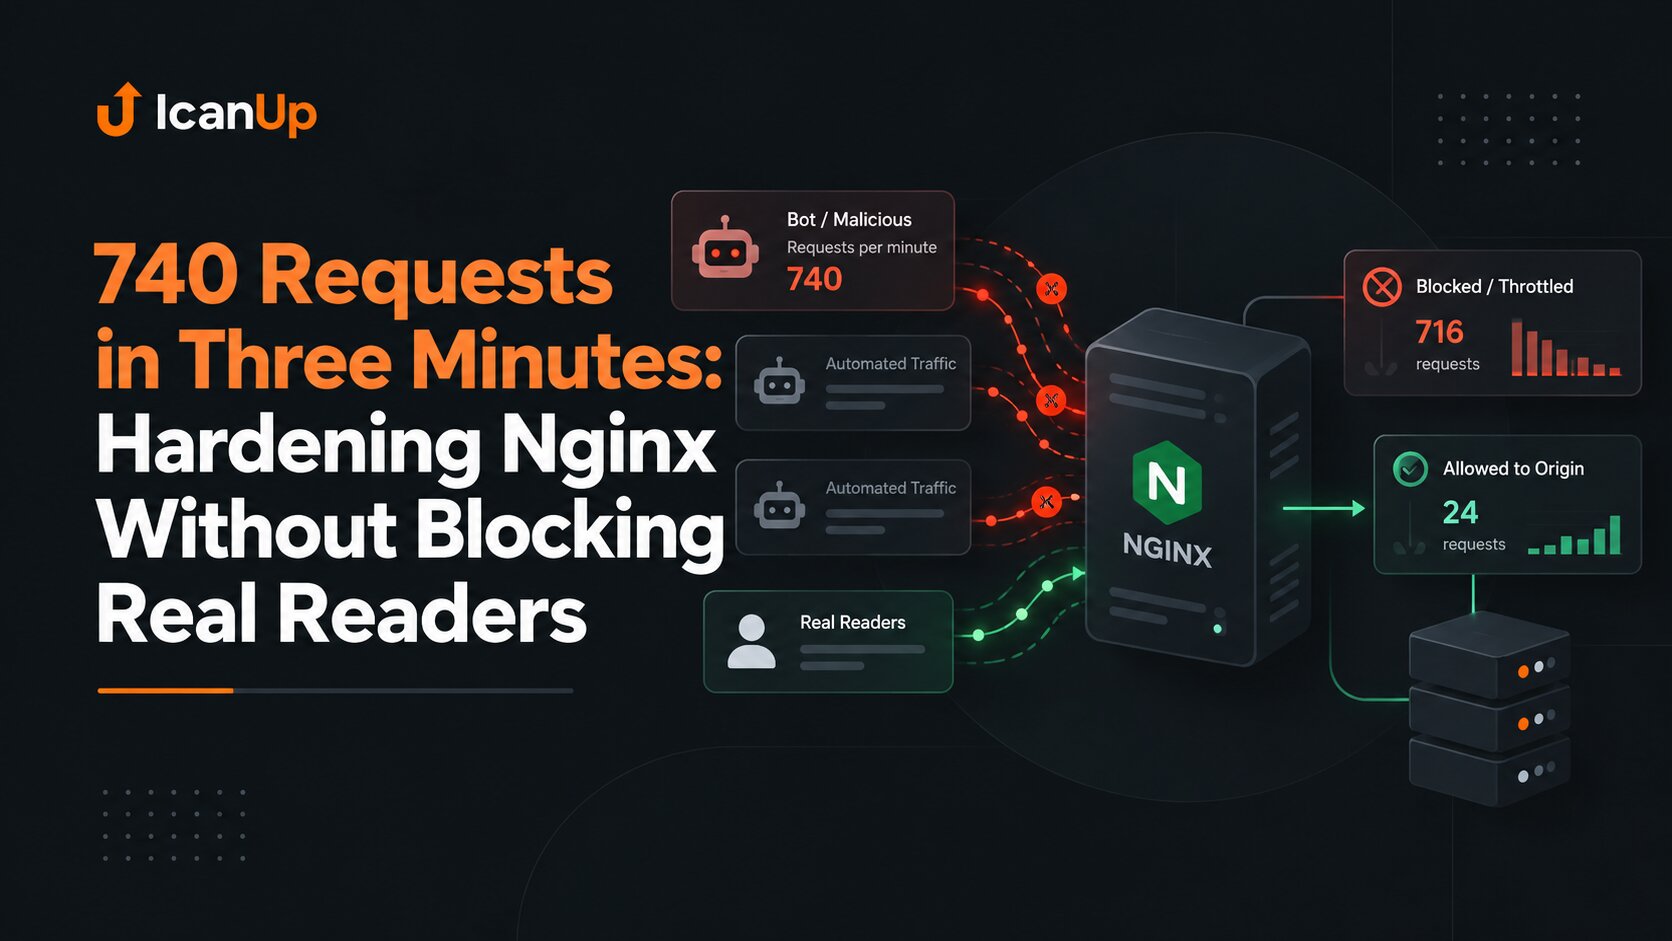
740 Requests in Three Minutes: Hardening Nginx Without Blocking Real Readers

After another traffic spike, I did not immediately block a country, User-Agent, or IP. I first correlated Laravel Analytics with Nginx logs, separated several independent traffic sources, verified Fail2ban behavior, and only then added Nginx rate limiting in dry-run mode.

51
how-i-protected-laravel-from-sensitive-path-scanners-with-nginx-and-fail2ban-cover.png
Nginx

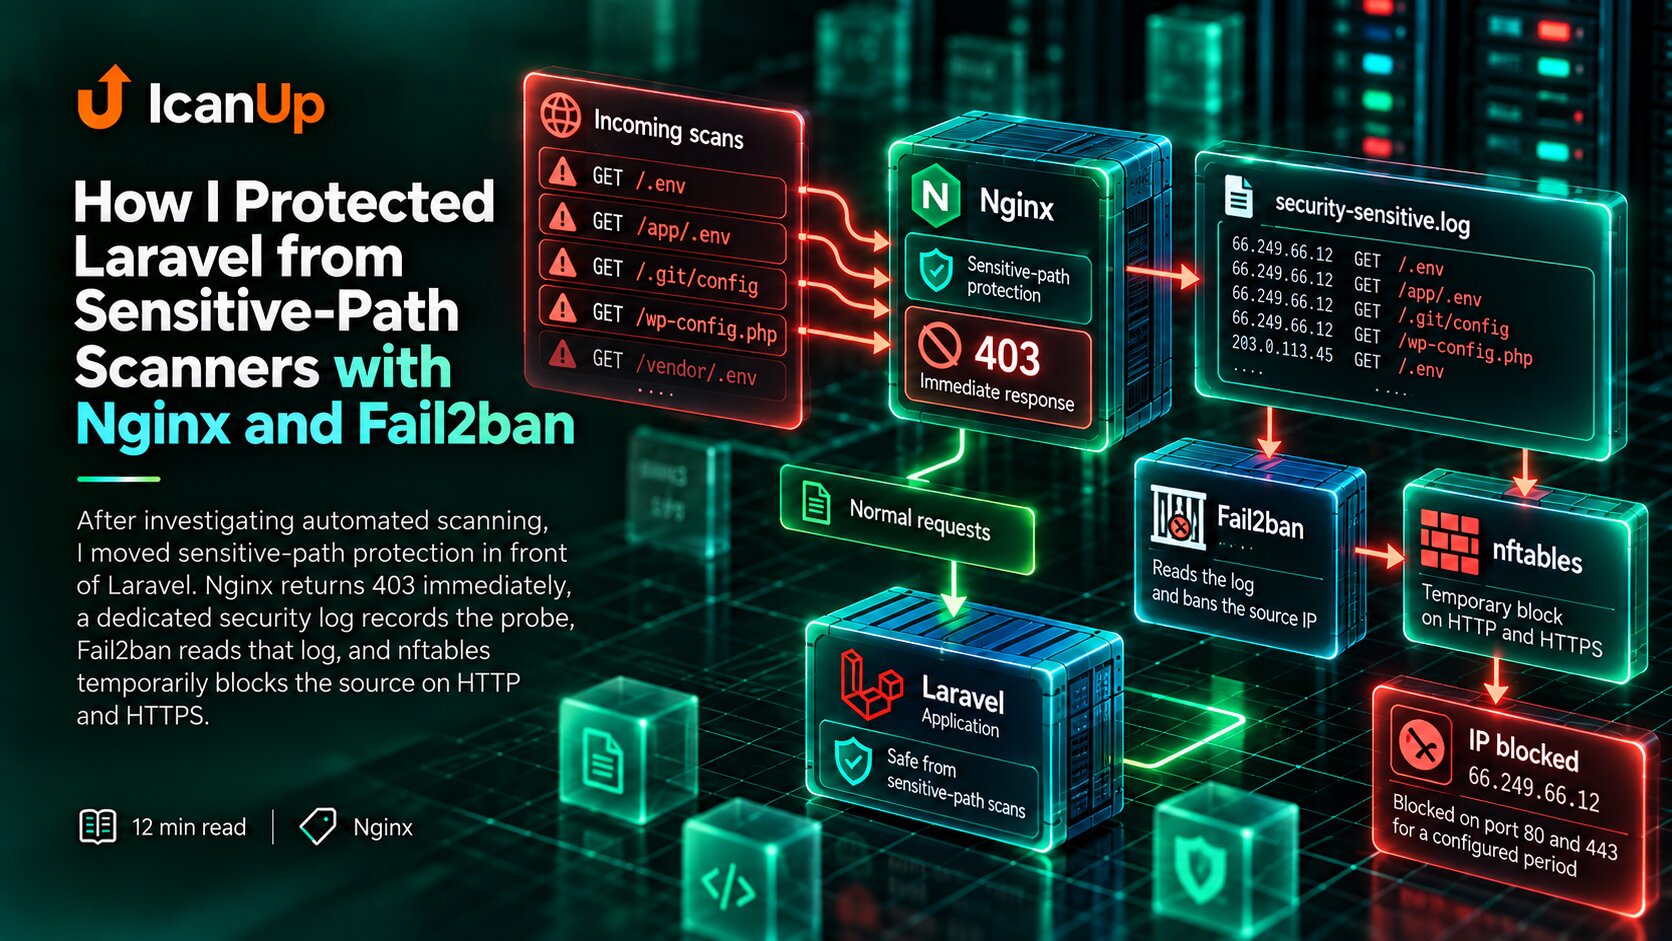
How I Protected Laravel from Sensitive-Path Scanners with Nginx and Fail2ban

After investigating automated scanning, I moved sensitive-path protection in front of Laravel. Nginx returns 403 immediately, a dedicated security log records the probe, Fail2ban reads that log, and nftables temporarily blocks the source on HTTP and HTTPS.

115
fake-googlebot-laravel-server-3300-requests-cover.png
Nginx

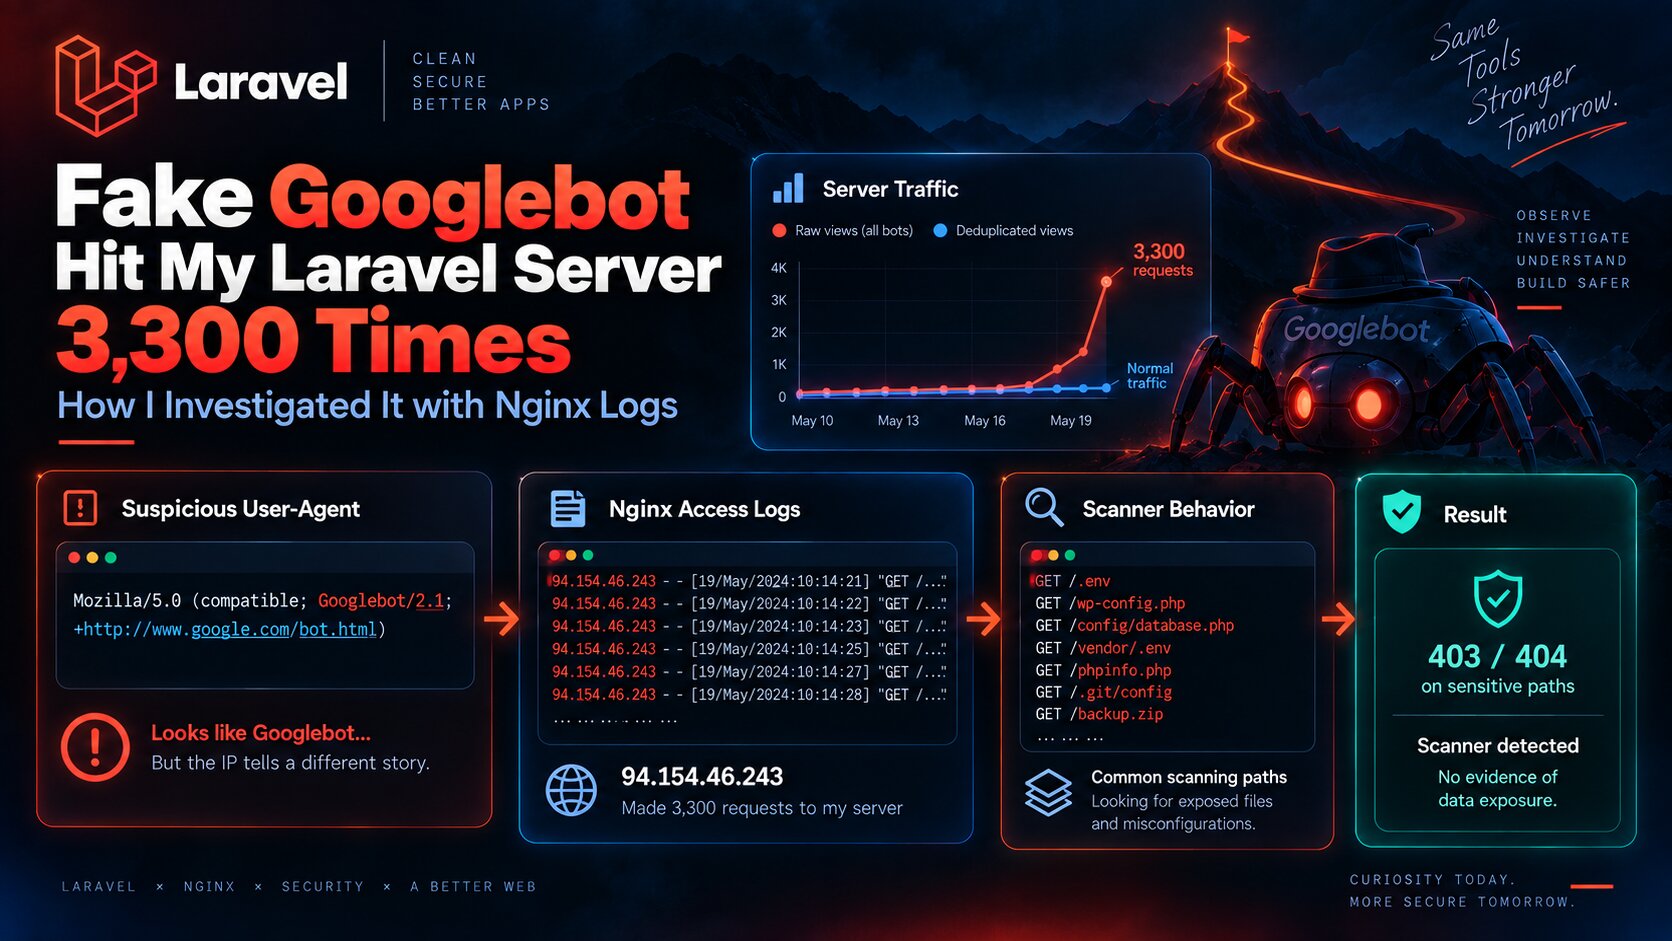
A Fake Googlebot Hit My Laravel Server 3,300 Times: How I Investigated It with Nginx Logs

On September 16, 2026, ICanUp analytics showed a sharp gap between raw and deduplicated views. Nginx access logs led me to an automated scanner impersonating Googlebot while probing thousands of .env, credential, and configuration paths. This article shows the investigation commands and why scanning activity is not the same as a breach.

212
nginx-trusted-headers-laravel-x-header-spoofing-cover.png
Nginx

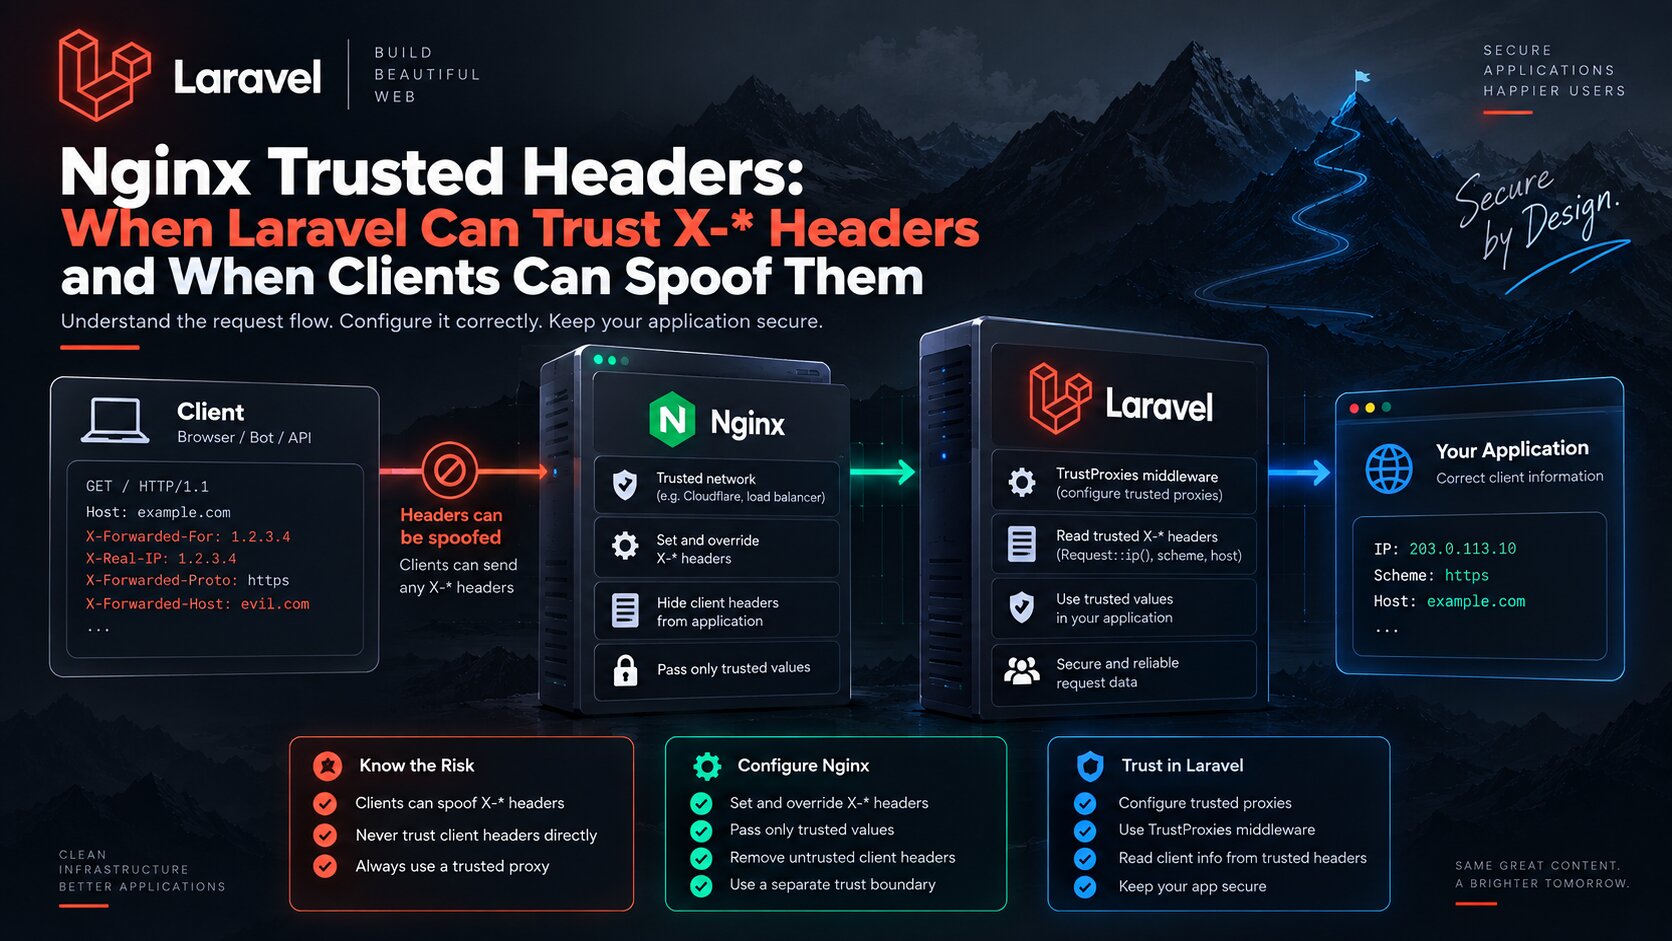
Nginx Trusted Headers: When Laravel Can Trust X-* Headers and When Clients Can Spoof Them

An HTTP header does not become trusted simply because its name starts with X-. This became important in ICanUp when Nginx started passing a GeoIP country code to Laravel. A client can send the same header itself, so the real security question is where the trust boundary lives and whether Nginx replaces client input before PHP sees it.

176
geoip-analytics-without-storing-ip-addresses-cover.png
Nginx

GeoIP Analytics Without Storing IP Addresses: Nginx + MaxMind + a Trusted Header

I needed country analytics in ICanUp without storing visitor IP addresses or calling an external GeoIP API on every page view. I moved country resolution to the Nginx and MaxMind infrastructure boundary, while Laravel receives only a normalized two-letter country code through a trusted internal header.

190
sectigo-ssl-nginx-dcv-renewal-debugging.png
Nginx

How I Renewed a Sectigo SSL Certificate in Nginx and Debugged DCV

While renewing a Sectigo SSL certificate, DCV stayed in progress even though the verification file returned 200 OK. I traced it to a stale token and different HTTP and HTTPS validation paths in Nginx, then completed the renewal safely.

222