A practical series on what to do after a PHP vulnerability is discovered: inspect the environment, safely update PHP and dependencies, clean Docker build cache and old layers, harden the server, and verify that the application still works correctly after security updates.
On October 21, 2026, the PHP Security Team disclosed CVE-2026-109618 and CVE-2026-109619, two critical vulnerabilities that can allow unauthenticated remote code execution. The issue is in the PHP runtime itself, not in application Composer dependencies.
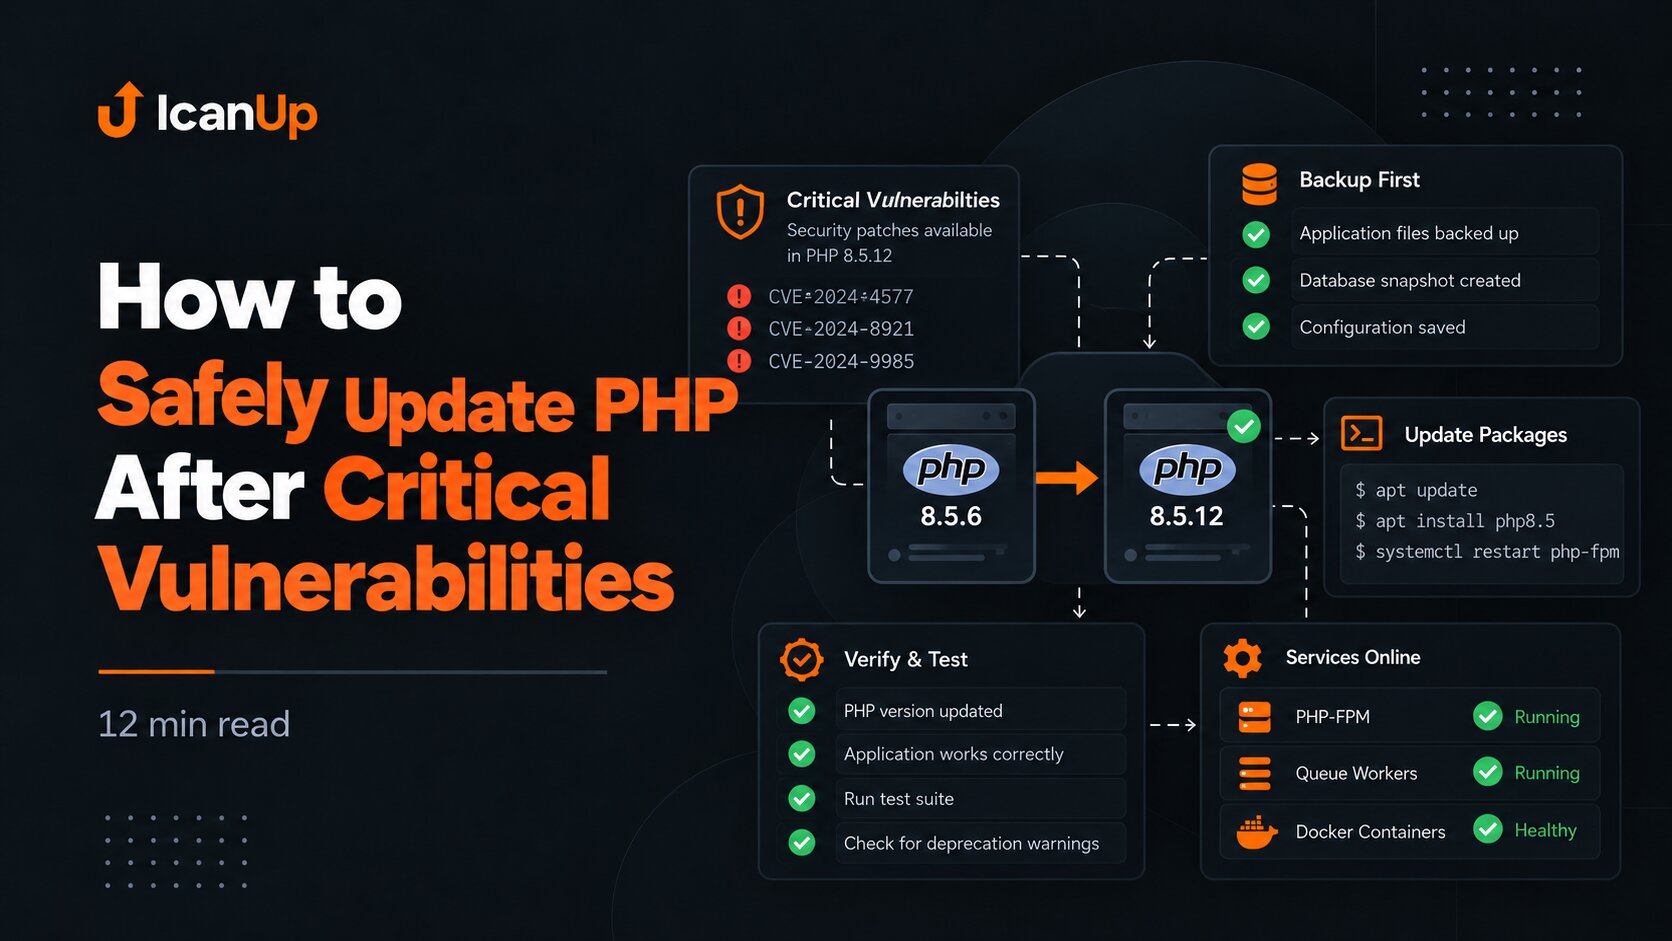
If a critical vulnerability is in PHP itself, updating Composer dependencies will not fix it. You need to inventory every environment, prepare backups, update the installed PHP packages, and then verify the site, PHP-FPM, queues, and Docker containers.